
The GeoServer open-source project has released a comprehensive security recap detailing a turbulent summer of 2026 marked by multiple Common Vulnerabilities and Exposures (CVEs), a high-profile zero-day incident, and a supply chain advisory. In response to these developments, project maintainers are strongly urging administrators to update their instances immediately. Organizations running vulnerable deployments are advised to apply the newly issued patches by upgrading to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6 depending on their specific production branches.
Throughout the lifecycle of the project, the GeoServer team has maintained a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are identified, investigated, and patched across both stable and maintenance releases prior to any public disclosure of CVE details. The fundamental goal of this policy is to ensure that system administrators and enterprise users have a fair and adequate window of opportunity to secure their infrastructure before malicious actors become aware of the specific technical details. However, maintaining this protective buffer became increasingly complex over the summer months due to unexpected disclosures and a notable influx of automated vulnerability reporting.
The most critical test of the project’s resilience occurred in August 2026, when GeoServer faced an active zero-day vulnerability. A zero-day exploit is defined as a security flaw that is actively targeted by attackers in the wild before a verified patch or official fix has been made publicly available. Prior to the public breach, the underlying problem had already been responsibly reported through private channels by several independent security researchers, allowing the core development team to schedule a formal fix as part of the upcoming GeoServer 3.0.1 release cycle.
Unfortunately, the controlled release timeline was disrupted when an unrelated third party—completely unconnected to the project leadership or the original research team—publicly disclosed the vulnerability on social media. The consequences of this uncoordinated leak were immediate and severe. Within hours of the social media post, automated security scans and malicious probes detecting the vulnerability were registered across the internet. The rapid escalation forced the project team to issue an emergency call to action across official user forums, while major cybersecurity news outlets picked up the story to warn the broader tech community. Project leadership acknowledged the swift reporting efforts of Ravie Lakshmanan, who first notified project leadership via the Open Source Geospatial Foundation, helping trigger the emergency response.
This chaotic zero-day episode dramatically reaffirmed the critical importance of adhering to coordinated vulnerability disclosure policies and underscored why timely updates are non-negotiable for enterprise software deployments. The incident prompted renewed discussions within the developer community about how third-party disclosures can inadvertently endanger thousands of production environments that rely on open-source geographic information system software.
The summer security updates also encompassed a series of previously published CVEs that were brought to light earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, the project published several security advisories affecting prior iterations, necessitating immediate patch deployment for users operating versions such as GeoServer 2.27.3, 2.26.4, and the foundational 2.27.0 release. These continuous updates highlight the ongoing maintenance overhead required to keep complex geospatial applications secure in modern threat environments.
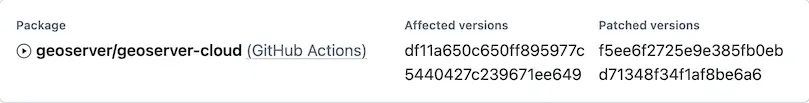
Adding to the complexity of the summer review, the GeoServer project encountered a supply chain advisory for the very first time. Supply chain advisories carry the inherent potential to undermine the cryptographic integrity and trustworthiness of software downloaded by end users. Because this specific infrastructure advisory did not correspond to an official release of the core GeoServer software package, it was officially classified under the label "geoserver/geoserver-cloud (GitHub Actions)" and did not qualify for a traditional CVE number.
Project leadership took pains to emphasize a critical reassurance for the user base: no official GeoServer releases were compromised or affected by this supply chain event. Standard GeoServer releases are compiled and distributed using a dedicated Jenkins build server that publishes verified artifacts directly to both SourceForge and the official Open Source Geospatial Foundation infrastructure, maintaining a secure separation from third-party cloud action pipelines.
Beyond traditional vulnerabilities and infrastructure concerns, the GeoServer project reported a noticeable surge in AI-assisted vulnerability reports. Like many prominent open-source software initiatives across the global technology landscape, maintainers are currently dealing with a massive wave of security alerts and bug submissions generated automatically through artificial intelligence tools. These AI-generated reports often present unique administrative challenges for open-source maintainers. They tend to be exceptionally verbose, demanding significant manual labor from core developers to review, parse, and determine whether the reported issues represent genuine security threats or are merely redundant duplicates.
To address this modern shift in vulnerability reporting, the project has established a general AI Policy and updated its comprehensive Security Policy hosted on GitHub. These policy documents formally acknowledge the widespread use of AI tools in security research and provide explicit guidance for researchers submitting AI-generated findings. The project has communicated that community members who utilize AI tools to scan for bugs can significantly assist the core security team by remaining actively available to clarify verbose reports, verify technical details, and test proposed fixes as vulnerabilities are addressed.
Sustaining the security and longevity of an open-source project of GeoServer’s scale requires continuous collaboration between developers, enterprise users, and institutional stakeholders. Project leadership has strongly encouraged organizations whose critical business operations depend on GeoServer to consider financial sponsorship or to allow their internal engineering staff to directly participate in the dedicated geoserver-security mailing list and working groups. Furthermore, the project is actively working to establish formal project membership pathways for public sector institutions and government agencies that frequently face administrative or legal restrictions regarding traditional financial sponsorship and direct community participation.
To maintain an adequate security posture, GeoServer operates on a time-boxed release cycle that spans a full calendar year, maintaining distinct categories for stable and maintenance versions. System administrators and IT professionals are strongly advised to upgrade their deployed GeoServer instances to a fully supported release at least once every twelve months to ensure uninterrupted access to critical security patches and bug fixes. Comprehensive instructions, migration paths, and technical guidance for upgrading existing versions are readily available within the official GeoServer User Guide.
Organizations or independent security researchers who discover potential vulnerabilities within the software are instructed to follow the project’s established disclosure guidelines. Rather than resorting to public channels or social media, researchers should submit vulnerability reports privately through the official GitHub security advisories interface, ensuring that the project maintains the opportunity to develop and distribute secure patches before public exposure occurs.




