
The GeoServer project team has released a comprehensive security review summarizing advisories published throughout the summer of 2026. The retrospective covers a high-pressure period for the widely used open-source geospatial software project, highlighting a notable zero-day vulnerability handled in August, a series of previously published Common Vulnerabilities and Exposures (CVEs), a non-release supply chain advisory, and an update to the project’s policy on AI-assisted vulnerability reporting.
For system administrators and organizations responsible for managing GeoServer instances, the immediate priority remains clear and urgent. Project maintainers advise all users to update their deployments to the newly issued versions: GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6, depending on which release branch their infrastructure currently utilizes.
The GeoServer project traditionally operates under a strict coordinated vulnerability disclosure policy. Under this framework, security vulnerabilities are thoroughly investigated, patched, and tested across both stable and maintenance release branches before any CVE details or technical descriptions are made public. The fundamental goal of this coordinated approach is to give system administrators, enterprise IT teams, and public sector agencies an adequate window of opportunity to apply necessary updates and secure their systems prior to wide public awareness. However, maintaining this protective buffer occasionally faces unexpected disruptions from external factors, as demonstrated by events over the summer.
The August Zero-Day Incident
In August 2026, the GeoServer project encountered a significant zero-day vulnerability—an active security flaw being exploited in the wild before an official patch could be broadly deployed. Prior to public exposure, the underlying problem had already been responsibly identified and reported privately by several independent security researchers. Project maintainers had scheduled a fix for this issue as part of the upcoming GeoServer 3.0.1 release cycle.
The zero-day crisis materialized when an unrelated third party, having no connection to the project leadership or the researchers who originally discovered the flaw, publicly disclosed the vulnerability details on social media channels. The consequences were immediate and severe. Within hours of the public social media post, automated security scanners and threat actors began probing internet-facing systems for the vulnerability.
The rapid escalation triggered swift media attention and prompted urgent advisories across user forums and communication channels managed by the Open Source Geospatial Foundation. Project leadership has formally extended its gratitude to security researcher Ravie Lakshmanan for initially notifying the foundation and helping orchestrate the subsequent response. The immediate deployment of GeoServer versions 3.0.1, 2.28.5, and 2.27.6 aimed to neutralize the threat. Project organizers noted that this turbulent experience forcefully reaffirmed the critical value of coordinated vulnerability disclosure and the necessity for administrators to apply updates promptly as soon as patches become available.
Previously Published CVEs and Release Cycles
The summer security recap also encompasses vulnerabilities addressed earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, the project published a distinct set of CVEs affecting earlier software branches, resulting in the rollout of maintenance fixes for GeoServer versions 2.27.3, 2.26.4, and initial updates for the 2.27.0 branch.
These ongoing updates underscore the complexity of maintaining a robust geospatial data server relied upon by academic institutions, government bodies, and enterprise mapping applications worldwide. GeoServer operates on a structured, time-boxed release cycle that spans a full calendar year, carefully balancing stable releases against long-term maintenance builds. Project guidelines recommend that organizations upgrade their deployed instances at least once a year to ensure continuous access to security patches and bug fixes. Comprehensive instructions for handling upgrades smoothly are maintained within the official user installation and upgrade guides.
Supply Chain Advisory and Infrastructure Integrity
In addition to traditional application-level vulnerabilities, the summer of 2026 brought the project’s first encounter with a supply chain advisory. Supply chain advisories inherently carry the potential to undermine user trust regarding the absolute integrity of downloaded software artifacts.
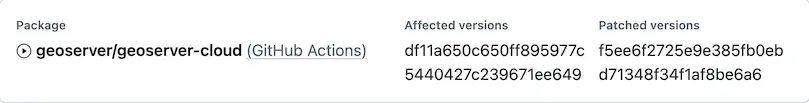
Because this specific incident involved a component of the continuous integration and delivery pipeline rather than a direct flaw in the source code of a software release, it was categorized specifically under the identifier "geoserver/geoserver-cloud (GitHub Actions)." Because the advisory did not correspond to an actual release of the GeoServer application itself, it did not qualify for a traditional CVE tracking number.
Project leadership emphasized a vital distinction for users: no official GeoServer releases were impacted by the supply chain event. Authentic GeoServer releases are produced exclusively through a dedicated Jenkins build server environment, which securely publishes verified artifacts directly to SourceForge and official Open Source Geospatial Foundation infrastructure.
Addressing the Surge in AI-Assisted Vulnerability Reports
Like many other prominent open-source software initiatives, the GeoServer development team has experienced a noticeable surge in security vulnerability reports generated with the assistance of artificial intelligence tools. These automated and AI-assisted submissions often present unique challenges for maintainers, frequently characterized by verbose technical descriptions, a high volume of false positives, and duplicate filings that require extensive manual triage.
To address this modern shift in security research methodology, the project has established a formal AI Policy and updated its overarching Security Policy. These policy adjustments acknowledge the reality of automated and AI-driven reporting tools while providing clear guidance for researchers utilizing them. Project maintainers have noted that because AI-generated reports tend to be exceptionally wordy, having reporters available on hand to clarify technical details, verify potential issues, and assist in testing proposed fixes is deeply appreciated. Navigating these submissions consumes substantial volunteer and developer time, meaning that any collaboration from the security community that streamlines the triage process directly benefits the security team’s workflow.
Community Involvement and Reporting Channels
Securing an enterprise-grade open-source project requires sustained collaboration and shared responsibility. Organizations whose operational workflows depend heavily on GeoServer are encouraged to explore options for supporting the project financially through official sponsorship programs or by enabling their engineering staff to participate directly in the geoserver-security working group. Furthermore, project organizers are actively working to establish formal project membership pathways for public institutions and governmental bodies that may face bureaucratic restrictions regarding direct financial sponsorship or open-source participation.
For individuals or organizations needing to report a newly discovered security vulnerability, the project maintains strict guidelines. Private vulnerability disclosures should be submitted securely through the GitHub security advisories interface, adhering to the protocols outlined in the official security policy document to ensure responsible handling before public disclosure.




