
The open-source geospatial community has faced a demanding season of security updates, culminating in a comprehensive recap of advisories published throughout the summer of 2026. The period brought to light a series of critical security challenges, including multiple Common Vulnerabilities and Exposures (CVEs), an unexpected zero-day exploit, and a supply chain incident affecting development infrastructure. These events have prompted project maintainers to issue urgent upgrade instructions, reinforce coordinated disclosure practices, and update institutional policies regarding the surge of AI-generated vulnerability reports.
Administrators responsible for managing GeoServer instances are being urged to apply the latest security patches immediately. The core project leadership has directed users to transition without delay to GeoServer version 3.0.1, version 2.28.5, or version 2.27.6, depending on their active branch. These releases contain essential fixes designed to close security gaps that could otherwise expose mapping servers and spatial data infrastructures to unauthorized access or exploitation.
GeoServer operates under a strict coordinated vulnerability disclosure policy. This framework is designed to ensure that security flaws are thoroughly investigated and patched across both stable and maintenance release lines before any technical details or CVE identifiers are made public. The underlying philosophy of this approach is to provide system administrators with adequate time to secure their environments, thereby mitigating the risk of widespread disruption before malicious actors can weaponize the discovered flaws. However, maintaining this balance of privacy and proactive defense can occasionally be upended by external factors beyond the control of the core development team.
August Zero-Day Disruption Highlights Disclosure Risks
The fragility of coordinated disclosure was starkly demonstrated in August 2026, when GeoServer encountered a high-profile zero-day vulnerability. An exploit was actively being utilized in the wild before an official patch could be publicly deployed. Prior to this public exposure, the underlying technical problem had already been identified and reported privately by several independent security researchers. Project maintainers had scheduled a comprehensive fix to coincide with the planned release of GeoServer 3.0.1.
The crisis unfolded when an unrelated third party—completely unconnected to the core GeoServer project and separate from the researchers who originally discovered the flaw—chose to disclose the vulnerability publicly on social media. The fallout was immediate and severe. Automated vulnerability scans and targeted exploit attempts were detected across the internet within hours of the social media post going live.
The rapid escalation forced the project team to accelerate their response, drawing significant media attention and triggering urgent warnings across user forums and mailing lists. Project leadership formally acknowledged the situation and expressed gratitude to security researcher Ravie Lakshmanan, who first notified project leadership through the Open Source Geospatial Foundation, helping coordinate the rapid emergency response.
This turbulent episode reaffirmed the critical importance of adhering strictly to coordinated vulnerability disclosure timelines. It also highlighted the vital need for organizations to apply new security updates the moment they are made available by the project maintainers, as delays can leave infrastructure dangerously exposed once information enters the public domain.
Addressing Previously Published CVEs and Release Cycles
The summer security review also encompassed a series of vulnerabilities disclosed earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, project maintainers published several CVEs affecting previous iterations of the software. These historical disclosures reinforce the continuous nature of software maintenance and the necessity of keeping enterprise mapping deployments aligned with actively supported product branches.
GeoServer relies on a structured, time-boxed release cycle that spans a full calendar year, carefully balancing both stable and maintenance release lines. Under this operational model, users are strongly advised to upgrade their deployed instances to a supported release at least once every twelve months. Regular maintenance ensures that administrative teams continue to receive critical security patches and performance improvements, minimizing the operational risks associated with running legacy software. Comprehensive guidance on managing these transitions is readily available through the official GeoServer user guide and documentation portals.
Supply Chain Advisory and Infrastructure Integrity
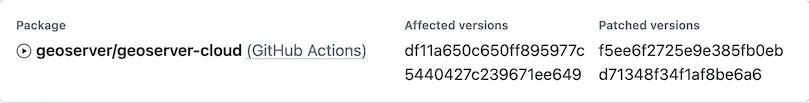
In addition to software-specific vulnerabilities, the GeoServer project encountered a notable supply chain advisory during the summer review period. This incident marked the first time the project has had to navigate an infrastructure-level advisory of this nature. Because the advisory specifically concerned the geoserver/geoserver-cloud component within GitHub Actions rather than a direct software release, it did not qualify for a traditional CVE identifier.
Crucially, project leadership confirmed that no official GeoServer software releases were compromised or affected by this supply chain event. GeoServer distributions continue to be compiled and published through secure channels, utilizing a dedicated Jenkins build server that distributes trusted artifacts to both SourceForge and the official infrastructure maintained by the Open Source Geospatial Foundation. This distinction underscores the resilience of the project’s primary release pipeline, even as developers remain vigilant against potential vulnerabilities within auxiliary cloud-based tooling and continuous integration workflows.
Managing the Wave of AI-Assisted Vulnerability Reports
Like many other prominent open-source software projects, the GeoServer maintainers have reported a noticeable surge in vulnerability submissions generated with the assistance of artificial intelligence. While automated tools can occasionally assist in identifying potential code anomalies, they frequently produce large volumes of verbose, ambiguous, or duplicate reports that require substantial human effort to analyze, verify, and filter.
To address this modern challenge, the project has established a formal AI Policy and updated its comprehensive Security Policy. These policy documents provide clear guidance for security researchers utilizing automated tools, emphasizing the need for precision, clarity, and constructive engagement. Reviewing AI-generated reports often demands considerable time from the core security team, making direct developer participation and willingness to test proposed fixes invaluable. The project has urged the community to support the security team by helping vet reports, verifying patches, and engaging constructively during the remediation process.
Strengthening Community Support and Collaboration
Sustaining a complex, widely utilized geospatial platform requires robust community backing and continuous resource allocation. Because GeoServer forms the backbone of countless enterprise geographic information systems across public and private sectors, project leaders have continually encouraged organizations relying on the software to invest back into its maintenance.
Companies and institutions utilizing GeoServer in production environments are encouraged to explore formal project sponsorship opportunities or support staff participation directly within the geoserver-security working groups. Furthermore, the project is actively working to establish new membership pathways via initiatives such as GSIP-243, designed specifically to accommodate public institutions and government agencies that may face administrative or legal restrictions regarding direct financial sponsorship or open-source contribution policies.
For those seeking to report newly discovered vulnerabilities securely, the project maintains a strict protocol. Security researchers are instructed to submit findings privately utilizing the GitHub security advisories mechanism outlined in the official repository security policy, ensuring that issues can be adequately evaluated, tested, and resolved before any public disclosure takes place.




