
The GeoServer project has issued a comprehensive security recap detailing a tumultuous summer of vulnerability disclosures, zero-day exploits, supply chain challenges, and an influx of automated reporting. At the center of the recent updates is an urgent call to action for administrators managing GeoServer instances worldwide: users must immediately upgrade their deployments to the newly released GeoServer versions 3.0.1, 2.28.5, or 2.27.6 to mitigate critical security risks.
The summer of 2026 has tested the resilience of the open-source geospatial project, highlighting both the persistent threat of uncoordinated disclosures and the changing landscape of software security research. By examining the timeline of recent advisories, project maintainers are emphasizing the vital importance of coordinated vulnerability disclosure and the need for organizations to maintain disciplined upgrade schedules.
August Zero-Day and the Dangers of Premature Disclosure
The most critical development of the summer occurred in August, when GeoServer was hit with a zero-day vulnerability—an active exploit in the wild with no immediately available official patch at the time of the leak. Prior to the public breach, the underlying security flaw had already been identified and reported privately by several independent researchers. Project maintainers had scheduled a fix for these vulnerabilities to coincide with the planned release of GeoServer 3.0.1.
However, the situation escalated rapidly when an unrelated third party publicly disclosed the vulnerability details on social media. The fallout was swift and immediate. Automated security scans searching for the specific vulnerability began hitting servers within hours of the public social media post. The speed of the hostile response triggered widespread concern, prompting immediate news coverage and urgent warnings broadcasted across the official GeoServer user forums.
Project leadership expressed gratitude to security researcher Ravie Lakshmanan, who first notified project leadership regarding the active exploitation via the Open Source Geospatial Foundation. In response to the crisis, development teams fast-tracked the release cycle, delivering GeoServer 3.0.1, GeoServer 2.28.5, and GeoServer 2.27.6 to plug the security gap. Maintainers noted that this intense episode serves as a stark reminder of why coordinated vulnerability disclosure policies are essential. When third parties bypass coordinated disclosure timelines, it denies system administrators the window of opportunity needed to apply patches before malicious actors weaponize the code.
Previously Published CVEs and Regular Release Cycles
The summer security updates also build upon vulnerabilities cataloged earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, developers published a series of Common Vulnerabilities and Exposures (CVEs) affecting older iterations of the software, specifically targeting GeoServer versions 2.27.3, 2.26.4, and 2.27.0.
These updates reflect GeoServer’s established operational model, which relies on a time-boxed release cycle operating across a yearly calendar. The project maintains parallel tracks for stable and maintenance releases to ensure that users have access to reliable software while receiving necessary security backports. Because vulnerabilities are routinely fixed for both stable and maintenance releases prior to the public publication of CVE details, the project aims to give administrators a fair head start on applying updates.
However, project maintainers stress that these security measures are only effective if organizations actively participate in the maintenance cycle. Administrators are strongly advised to upgrade their GeoServer installations to a supported release at least once a year to ensure continuous receipt of vital security patches and bug fixes. Guidance for navigating these upgrades is comprehensively documented within the official GeoServer user guide.
Navigating Supply Chain Advisories
In addition to direct software vulnerabilities, the GeoServer project faced a unique challenge over the summer concerning a supply chain advisory. Supply chain advisories carry inherent risks because they have the potential to compromise the integrity of downloaded software components, making them a focal point for modern cybersecurity defense.
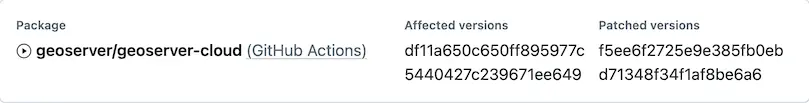
This incident marked the first time the GeoServer project has had to navigate an infrastructure-level advisory of this nature. Because the issue affected the build pipeline rather than the source code of a specific software release, project maintainers classified the advisory under the designation "geoserver/geoserver-cloud (GitHub Actions)." Because it did not correspond directly with an official release of the GeoServer application, it did not qualify for a traditional CVE number.
Crucially, project leadership confirmed that no official GeoServer releases were compromised or affected by the incident. Standard GeoServer releases are compiled and published using a dedicated Jenkins build server that distributes trusted artifacts to both SourceForge and OSGeo infrastructure. The transparency surrounding this advisory highlights the project’s commitment to maintaining rigorous oversight over its entire software delivery pipeline.
Managing the Wave of AI-Assisted Vulnerability Reports
Like many prominent open-source software projects across the global technology ecosystem, GeoServer has experienced a significant surge in vulnerability reports generated with the assistance of artificial intelligence tools. While AI technologies have democratized security research, they have also introduced new administrative bottlenecks for maintainers.
Automated and AI-assisted reports are frequently characterized by their extreme verbosity, requiring substantial human effort to parse, verify, and determine authenticity. Reviewing these extensive submissions consumes considerable developer time, particularly when sorting through redundant or duplicate claims. To address this evolving paradigm, the project has established a dedicated general AI policy and updated its core security policy to explicitly acknowledge the use of AI tools in vulnerability discovery and reporting.
The updated policies provide clear guidelines for researchers utilizing automated tools, asking them to remain available to clarify complex reports and assist maintainers in testing and verifying proposed fixes. Reducing the friction involved in processing these submissions helps the geoserver-security team direct their limited resources toward genuine threats rather than sorting through unverified, AI-generated noise.
Community Support and Secure Reporting Practices
Sustaining the security and ongoing development of an enterprise-grade open-source project requires active community engagement. Project maintainers have reiterated calls for organizations whose operational infrastructure depends on GeoServer to consider financial sponsorship or direct staff participation in geoserver-security operations. Furthermore, the project is actively working to establish formal project membership pathways for public institutions and governmental agencies that may face institutional restrictions regarding direct financial sponsorship or external participation.
For organizations and security researchers seeking to report newly discovered vulnerabilities, the project mandates adherence to established channels. Private vulnerability disclosures should be submitted securely using GitHub security advisories as outlined in the official GeoServer security policy. By combining strict adherence to coordinated disclosure, proactive annual upgrading, and responsible reporting standards, the GeoServer community continues to fortify its geospatial platform against an increasingly complex threat landscape.




