
As the software development landscape continues to evolve, open-source projects face a shifting array of security challenges, ranging from rapid-fire zero-day disclosures to the growing influx of automated vulnerability submissions. The GeoServer project has released a comprehensive security recap detailing the advisories published over the summer of 2026. The summary covers recently published Common Vulnerabilities and Exposures (CVEs), a notable supply chain advisory affecting components outside core releases, and vital updates to the project’s security policies to address the rise of artificial intelligence in vulnerability research.
For administrators and organizations responsible for deploying and maintaining GeoServer instances, the most immediate and critical takeaway from the summer update is the urgent need to patch. The project team has strongly urged users to update their deployments to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6 immediately to protect against recently exploited vulnerabilities.
The GeoServer project maintains a strict coordinated vulnerability disclosure policy. Under this framework, security flaws are thoroughly investigated, and fixes are developed and tested for both stable and maintenance release lines before any CVE details are made public. The underlying philosophy of this approach is to provide system administrators, enterprise IT teams, and institutional maintainers with a fair and adequate window of opportunity to apply security patches prior to the broader public disclosure of exploit mechanics. Unfortunately, maintaining this controlled timeline can be disrupted by external actors, as the project recently witnessed during the summer months.
The August Zero-Day Incident
In August, the GeoServer project encountered a serious zero-day vulnerability—an active exploit in the wild for which no official patch had yet been publicly released by the project team. Prior to this public exposure, the underlying problem had already been responsibly reported through private channels by several independent security researchers. A formal fix was already scheduled to be bundled into the upcoming GeoServer 3.0.1 release, adhering to the project’s standard remediation pipeline.
The zero-day situation escalated rapidly when an unrelated third party, unconnected to either the project leadership or the original reporting researchers, publicly disclosed the vulnerability details on social media. The fallout from this uncoordinated disclosure was immediate and severe. Automated scanning tools and malicious actors began actively probing for the vulnerability within hours of the public social media post, turning a managed remediation process into an emergency response situation.
The sheer velocity of the threat response required extraordinary measures. The incident quickly attracted external news coverage and prompted an urgent call to action across official user forums and communication channels. Project leadership expressed gratitude to reporter Ravie Lakshmanan, who first notified project leadership regarding the active exploitation via the Open Source Geospatial Foundation.
This stressful experience forcefully reaffirmed the absolute necessity of following coordinated vulnerability disclosure policies. The incident highlights why urging all users to update their software promptly upon the release of new security patches is vital for maintaining the integrity of geospatial infrastructure worldwide.
Previously Published CVEs and Release Tracking
The summer security updates also incorporated vulnerabilities addressed earlier in the cycle. Back on June 11, 2026, alongside the major release of GeoServer 3.0.0, the project published several CVEs affecting earlier iterations of the software. These historical updates underscore the continuous maintenance effort required by core developers to keep complex mapping and geospatial data servers secure against newly discovered attack vectors across multiple active release branches.
Supply Chain Advisory and Infrastructure Integrity
In addition to software code vulnerabilities, the project addressed a supply chain advisory during the summer review period. Supply chain advisories carry inherent risks because they have the potential to undermine the baseline integrity of the software packages that users download and deploy within their networks.
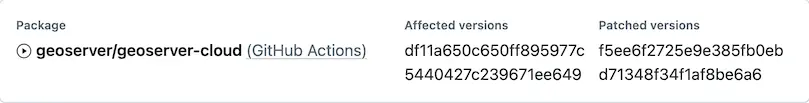
Significantly, this marked the first time the GeoServer project had to work through an infrastructure-level advisory of this nature. Because the issue did not correspond to a standard source code release of GeoServer itself, it was formally designated as a "geoserver/geoserver-cloud (GitHub Actions)" advisory. Consequently, it did not qualify for a traditional CVE number.
Project maintainers emphasized a crucial distinction for users: no official GeoServer software releases were affected by this supply chain concern. Standard GeoServer releases are compiled and published using an isolated Jenkins build server, which then distributes the verified artifacts to both SourceForge and official Open Source Geospatial Foundation infrastructure. This separation of build environments helped ensure that end-user installations remained secure despite the upstream cloud infrastructure advisory.
AI-Assisted Vulnerability Reports and Policy Updates
Like many other prominent open-source software communities, the GeoServer project has experienced a noticeable wave of vulnerability reports generated with the assistance of artificial intelligence tools. While automated tooling can sometimes assist in identifying potential code anomalies, these AI-generated submissions frequently introduce unique administrative hurdles for maintainers.
To adapt to this technological shift, the project has established a general AI Policy and updated its comprehensive Security Policy. These policy updates formally acknowledge the widespread use of AI generation tools in security research and provide clear guidance for researchers submitting findings.
A primary challenge with AI-assisted vulnerability reports is that they are frequently extremely verbose while occasionally lacking deep contextual verification. Project maintainers note that having reporters on hand to clarify complex, machine-generated narratives is greatly appreciated. Reviewing these reports consumes substantial time from core developers, particularly when trying to determine if a lengthy submission represents a novel security flaw or is simply a duplicate of an already known issue.
Furthermore, the review process moves much more smoothly when reporters are positioned to test and verify proposed fixes as developers work to address them. Any assistance that external contributors can provide to lighten the workload of the dedicated GeoServer security team makes a significant difference in how rapidly the project can respond to emerging threats.
Community Support and Upgrade Cadence
Securing a complex open-source project like GeoServer requires sustained collaboration and resources from the broader community. Organizations that rely heavily on GeoServer for critical spatial data infrastructure are encouraged to consider financial sponsorship through the project’s official channels, or to have their internal staff directly participate in the work of the geoserver-security team. Additionally, the project is actively exploring the establishment of formal project membership structures to accommodate public institutions and government agencies that frequently face administrative restrictions regarding direct financial sponsorship and participation.
To maintain robust security posture, administrators must remain vigilant about their upgrade schedules. GeoServer operates on a structured, time-boxed release cycle that maintains both stable and maintenance releases over the course of a year. Security experts advise organizations to upgrade their GeoServer installations to a supported release at least once a year to ensure they continue receiving timely security patches and bug fixes. Comprehensive instructions and best practices for transitioning between versions are documented in the official user guide for upgrading existing installations.
For organizations and security researchers seeking to report new vulnerabilities responsibly, the project maintains strict guidelines. Security issues should never be disclosed publicly before a coordinated fix is ready. Instead, reports must be submitted privately through GitHub security advisories in accordance with the project’s published security policy, ensuring that the global GeoServer community is given adequate time to protect its users.




