
Administrators of GeoServer instances worldwide are being urged to apply immediate software updates following a turbulent summer of security disclosures, highlighted by an unpatched zero-day vulnerability exploited in the wild. The GeoServer project team has released a comprehensive security recap detailing the recent wave of Common Vulnerabilities and Exposures (CVEs), a notable supply chain advisory involving project infrastructure, and a newly updated security policy designed to handle the growing influx of AI-assisted vulnerability reports.
For system administrators responsible for maintaining geospatial data infrastructure, the immediate call to action is clear: installations should be upgraded immediately to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6. These critical releases contain essential patches designed to secure servers against active threats and maintain the integrity of geographic information systems globally.
The GeoServer project historically adheres to a strict and coordinated vulnerability disclosure policy. Under this framework, vulnerabilities are meticulously patched across both stable and maintenance releases prior to the public publication of any CVE details. The overarching goal of this coordinated approach is to provide system administrators, organizations, and institutional users with an adequate window of opportunity to update their software environments before malicious actors can weaponize the disclosed flaws. However, maintaining this protective buffer relies heavily on adherence from all participating parties.
August Zero-Day
The delicate balance of coordinated disclosure was tested in August 2026, when GeoServer encountered a serious zero-day vulnerability—an active exploit occurring in the wild without a pre-existing public fix. Prior to this public exposure, the underlying problem had already been privately reported to project maintainers by several independent security researchers. A comprehensive fix had already been scheduled for inclusion in the forthcoming GeoServer 3.0.1 release.
The zero-day situation escalated rapidly when an unrelated third party, having no connection to the project leadership or the original reporting researchers, publicly disclosed the technical details of the vulnerability on social media. The consequences of this premature disclosure were instantaneous and severe. Automated scans searching for vulnerable GeoServer instances were detected by security monitors within mere hours of the social media post going live.
The remarkable speed with which malicious actors mobilized triggered widespread media coverage and prompted project maintainers to issue an urgent call to action across official user forums. Project leadership formally acknowledged the swift reporting efforts of Ravie Lakshmanan, who first notified project leadership through the Open Source Geospatial Foundation. The prompt release of GeoServer 3.0.1, alongside updated maintenance versions 2.28.5 and 2.27.6, helped mitigate the immediate danger. Nonetheless, the incident powerfully reaffirmed the critical importance of respecting coordinated vulnerability disclosure policies and emphasized why administrators must apply patches the moment they are made available.
Previously Published CVEs
The summer security review also encompasses a series of vulnerabilities published earlier in the season. On June 11, 2026, alongside the major rollout of the GeoServer 3.0.0 release, a batch of CVEs was brought to light. These disclosures affected earlier iterations of the software, prompting swift responses from the development community to ensure that users operating stable branches as well as legacy maintenance lines were not left exposed to known vectors of attack.
Managing vulnerabilities across multiple concurrent branches remains a complex undertaking for open-source geographic software projects. The continuous cycle of identifying, verifying, and backporting fixes to active maintenance branches like GeoServer 2.27.x and 2.26.x highlights the continuous effort required by core developers and community volunteers to keep enterprise-grade mapping servers secure.
Supply Chain Advisory
In addition to traditional application-level vulnerabilities, the project recently navigated its first encounter with a supply chain advisory. Supply chain security alerts carry unique implications because they have the potential to undermine the baseline integrity of the software packages downloaded by end users.
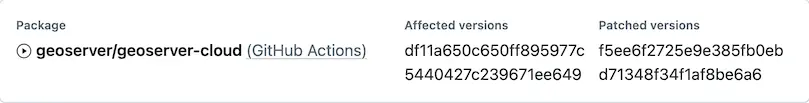
Because this specific incident did not correspond directly to a standard source code release of GeoServer, it did not qualify for a traditional CVE number. Instead, project maintainers formally categorized the advisory under the designation "geoserver/geoserver-cloud (GitHub Actions)."
Crucially, project leadership confirmed that no official GeoServer software releases were compromised or affected by this supply chain event. Standard GeoServer releases are compiled and published through a secure Jenkins build server, which systematically distributes official artifacts to both SourceForge and the core OSGeo infrastructure. This separation of infrastructure safeguards official releases from localized CI/CD pipeline anomalies.
AI-assisted Vulnerability Reports
Like many prominent open-source software communities, the GeoServer project has experienced a noticeable surge in vulnerability reports generated with the assistance of artificial intelligence tools. While automated and AI-driven analysis can sometimes assist in identifying edge cases, it frequently generates a high volume of verbose, speculative, or duplicate submissions that require significant human review to validate.
To address this modern challenge, the project has established a dedicated AI Policy and updated its comprehensive Security Policy hosted on GitHub. These policy updates formally acknowledge the integration of AI tools into the vulnerability discovery ecosystem and provide clear operational guidance for submitters.
Project maintainers note that reviewing automated and AI-generated reports demands considerable time from the core security team. Consequently, community members who submit such reports are strongly encouraged to remain actively engaged to clarify ambiguities, assist in identifying duplicate entries, and help test and verify proposed patches. Active community participation significantly lightens the administrative and technical burden on the small team handling security triage.
Community Support and Upgrades
Securing a widely deployed open-source project like GeoServer requires sustained collaboration between core developers, institutional users, and commercial organizations. Organizations that rely heavily on GeoServer for critical spatial data infrastructure are encouraged to support the project financially through sponsorship programs or by allowing staff members to participate directly in the geoserver-security working groups. Furthermore, the project is actively working to establish formal project membership pathways for public institutions and government agencies that frequently face administrative or legal restrictions regarding corporate sponsorship and direct participation.
To maintain robust security postures, administrators are advised to follow the project’s time-boxed release cycle. GeoServer routinely maintains both stable and maintenance release branches over the course of each year. Users are strongly urged to upgrade their deployments to a supported version at least once every twelve months to ensure they continue receiving vital security patches and bug fixes. Comprehensive instructions for transitioning between versions are documented within the official GeoServer User Guide.
Anyone discovering a potential security vulnerability within the software is encouraged to review the project’s official security policy for instructions on how to submit reports privately through GitHub security advisories, ensuring responsible disclosure before public awareness can be exploited.




