
The GeoServer project has issued a comprehensive security recap detailing a turbulent summer of 2026, which included managing a high-profile zero-day vulnerability, addressing a series of Common Vulnerabilities and Exposures (CVEs), navigating a supply chain advisory, and updating project policies to handle a surge in AI-generated security reports. Administrators running GeoServer instances are being urged to update immediately to the latest versions—GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6—to secure their systems against active exploitation.
The open-source geospatial project strictly adheres to a coordinated vulnerability disclosure policy, ensuring that security flaws are patched in both stable and maintenance releases before any technical details or CVE identifiers are made public. The fundamental goal of this strategy is to provide system administrators and organizations worldwide with an adequate window of opportunity to apply updates safely before malicious actors can weaponize the information. However, maintaining this protective buffer proved challenging over the summer months, leading to an unexpected zero-day emergency that tested the responsiveness of the project leadership and the broader user community.
August Zero-Day
In August, the GeoServer project encountered a critical zero-day vulnerability—an active exploit in the wild operating without a known, publicly available fix at the time of discovery. The underlying flaw had already been reported privately through appropriate channels by several independent researchers, and a formal patch had been scheduled for inclusion in the upcoming GeoServer 3.0.1 release.
The crisis escalated when a third-party entity, entirely unconnected to the project or the original researchers, publicly disclosed the vulnerability details on social media. The consequences were immediate and severe. Automated scans searching for vulnerable instances were detected across the internet within hours of the public social media post. The remarkable speed of these automated attacks triggered widespread media coverage and prompted project leaders to issue urgent upgrade warnings across official user forums. Project leadership expressed gratitude to security researcher Ravie Lakshmanan, who first notified project leadership regarding the active exploitation via the Open Source Geospatial Foundation.
With the release of GeoServer 3.0.1, GeoServer 2.28.5, and GeoServer 2.27.6, the immediate threat has been addressed, but the incident has powerfully reaffirmed the critical importance of coordinated vulnerability disclosure. The project continues to urge all users to apply updates immediately whenever new releases become available to mitigate the risks associated with premature public disclosures.
Previously Published CVEs
The summer security review also encompasses vulnerabilities disclosed earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, the project published a series of CVEs affecting older branches, requiring prompt remediation across various deployments running versions such as GeoServer 2.27.3, 2.26.4, and 2.27.0. These routine security updates underscore the continuous maintenance effort required to protect complex geospatial data infrastructures from evolving cyber threats.
Supply Chain Advisory
Beyond direct application vulnerabilities, the project recently confronted its first encounter with a software supply chain advisory. Because supply chain incidents have the potential to compromise the integrity of downloaded software packages, transparency is vital for maintaining user trust.
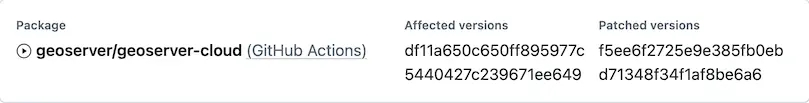
The project noted that this particular advisory was categorized specifically under "geoserver/geoserver-cloud (GitHub Actions)" because it did not correspond to a standard release of GeoServer itself, and therefore did not qualify for a traditional CVE number. Crucially, project maintainers confirmed that no official GeoServer releases were affected by the supply chain issue. Standard GeoServer releases continue to be compiled using an isolated Jenkins build server that publishes verified artifacts directly to SourceForge and official OSGeo infrastructure, shielding core user downloads from upstream pipeline compromises.
AI-Assisted Vulnerability Reports
Like many other prominent open-source software projects, the GeoServer maintainers are currently managing a significant influx of vulnerability reports generated with the assistance of artificial intelligence tools. While these technologies can sometimes aid in security analysis, they frequently produce a high volume of verbose, ambiguous, or inaccurate submissions.
To adapt to this shifting landscape, the project has established a general AI Policy and updated its comprehensive Security Policy. These documents formally acknowledge the utilization of AI tools in vulnerability research and provide clear guidance for researchers. Reviewing AI-assisted reports demands substantial time and technical effort from maintainers, particularly when determining authenticity, filtering out duplicate submissions, or separating genuine security flaws from theoretical noise. The project has emphasized that researchers who submit AI-generated reports should remain actively available to clarify details, test proposed patches, and assist the geoserver-security team in verifying fixes.
Community Support and Participation
Securing an enterprise-grade open-source project requires sustainable resources and active community involvement. Organizations whose operations depend heavily on GeoServer are encouraged to consider financial sponsorship or to allow their internal technical staff to participate directly in geoserver-security operations. Furthermore, the project is working to establish formal project membership pathways for public institutions and government agencies that often face regulatory restrictions regarding direct financial sponsorship and corporate participation.
Upgrade Frequency and Maintenance
GeoServer operates on a structured, time-boxed release cycle, systematically maintaining both "stable" and "maintenance" branches throughout the course of a year. To maintain robust defense postures, administrators are strongly advised to upgrade their GeoServer installations to a supported release at least once every twelve months to ensure continuous access to critical security patches and bug fixes. Comprehensive instructions for transitioning between versions are documented in the official user guide under upgrade procedures.
Reporting Vulnerabilities
Security researchers and community members who discover potential security issues within GeoServer are reminded to follow responsible disclosure guidelines. Detailed instructions for reporting vulnerabilities privately using GitHub security advisories can be found directly within the project’s official security policy documentation.




