
The GeoServer project has issued a comprehensive security recap detailing a volatile summer of 2026, highlighted by a high-profile zero-day vulnerability, a series of previously published Common Vulnerabilities and Exposures (CVEs), and a supply chain advisory. The developments have also prompted the open-source geospatial project to update its official security policies regarding the influx of AI-assisted vulnerability disclosures.
Administrators and organizations responsible for managing GeoServer instances are being urged to apply the latest security patches immediately. The core recommendation from project maintainers is to update installations without delay to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6, depending on which stable or maintenance branch the organization currently operates.
The GeoServer project traditionally adheres strictly to a coordinated vulnerability disclosure policy. Under this framework, security flaws are identified, analyzed, and fixed across both stable and maintenance release branches before any technical details or CVE identifiers are made public. This practice is designed to give system administrators a vital window of opportunity to patch their environments before malicious actors can weaponize the flaws. However, events over the summer put this coordinated approach to a severe test.
August Zero-Day
In August 2026, the GeoServer project faced a critical zero-day vulnerability—an active exploit functioning in the wild with no pre-existing official patch available at the moment of public disclosure. Prior to this public leak, the underlying problem had already been responsibly reported through private channels by several independent security researchers, and a fix had been carefully scheduled for inclusion in the upcoming GeoServer 3.0.1 release.
The crisis escalated rapidly when a third-party entity, entirely unconnected to the project leadership or the original reporting researchers, publicly disclosed the vulnerability details on social media. The fallout was instantaneous. Automated network scans seeking to identify and compromise vulnerable GeoServer instances were detected within hours of the public social media post.
The velocity of the exploitation attempts triggered widespread concern, prompting immediate news coverage and urgent broadcast alerts across official user forums. Project leadership formally acknowledged the swift escalation and extended gratitude to researcher Ravie Lakshmanan for initially notifying project leadership via the Open Source Geospatial Foundation. The prompt rollout of GeoServer 3.0.1, alongside updated maintenance versions 2.28.5 and 2.27.6, aimed to stem the tide of potential compromises. According to project representatives, this turbulent episode starkly reaffirms the critical importance of respecting coordinated vulnerability disclosure policies and underscores why administrators must apply patches immediately upon release.
Previously Published CVEs
The summer security recap also cataloged vulnerabilities addressed earlier in the season. On June 11, 2026, alongside the major release of GeoServer 3.0.0, a series of CVEs were published to address various security shortcomings across legacy and current branches. These disclosures required downstream users to migrate or patch across versions such as GeoServer 2.27.3, 2.26.4, and the foundational 2.27.0 release. The continuous cycle of patching highlights the ongoing challenge of maintaining security hygiene within complex geospatial software ecosystems.
Supply Chain Advisory
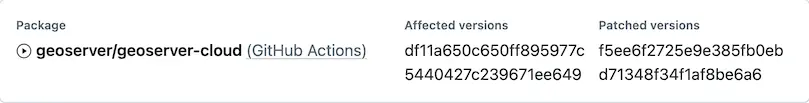
Adding to the complexity of the summer review, the project encountered its first-ever infrastructure-level supply chain advisory. Because supply chain vulnerabilities have the potential to undermine the fundamental integrity of downloadable software artifacts, any related warning commands immediate attention from the community.
Project leaders clarified that this particular advisory was uniquely categorized under "geoserver/geoserver-cloud (GitHub Actions)" because it did not correspond to a standard software release of GeoServer itself, and thus did not meet the criteria for receiving a formal CVE number. Crucially, the project confirmed that no official GeoServer releases were compromised or affected by the incident. Standard GeoServer releases continue to be built securely using a dedicated Jenkins build server that publishes verified artifacts directly to SourceForge and the official OSGeo infrastructure.
AI-Assisted Vulnerability Reports
Compounding the operational workload of the security team over the summer has been an unprecedented surge in security vulnerability reports generated with the assistance of artificial intelligence tools. Like numerous other open-source software projects, GeoServer is navigating a new landscape where AI systems generate large volumes of speculative security findings.
To address this shifting dynamic, the project has established a dedicated general AI policy and updated its core GitHub security policy. These guidelines formally acknowledge the utilization of AI tools in vulnerability research and provide explicit instructions for researchers employing them. Project maintainers emphasize that AI-generated reports are frequently very verbose, making human availability and direct clarification highly valuable. Reviewing these extensive submissions consumes considerable time, particularly when filtering out duplicate reports or determining validity. Community members who possess the capability to test, verify, and assist with fixes are strongly encouraged to support the overworked geoserver-security team.
Community Support and Maintenance
As the GeoServer ecosystem confronts these modern security challenges, project leaders are actively calling upon the user community for reinforcement. Organizations that rely heavily on GeoServer for critical geospatial infrastructure are urged to consider financial sponsorship or direct staff participation in security-focused initiatives. Furthermore, the project is currently working to establish formal project membership pathways for public institutions that may face bureaucratic restrictions regarding traditional sponsorship and participation models.
To maintain robust security postures over the long term, administrators are reminded that GeoServer operates on a structured, time-boxed release cycle that maintains both stable and maintenance lines over the course of any given year. Users are strongly advised to upgrade their deployments to a supported release at least once every twelve months to ensure uninterrupted access to security patches and vulnerability fixes. Detailed instructions and upgrade pathways are continuously updated within the official GeoServer user installation guides.
Anyone discovering a potential security vulnerability within the platform is directed to consult the official security policy on GitHub for instructions on how to submit reports privately through secure channels.




