Security experts have been sounding the alarm for years about the hidden dangers of using generic, off-brand TV streaming boxes that promise unlimited, premium content streaming for a low, one-time fee. While previous investigations primarily warned that these devices secretly rent out the user’s home internet connection to unknown strangers as residential proxies, a groundbreaking new security analysis reveals an even more sprawling and deceptive operation. These devices routinely spoof themselves as popular mobile phones, automatically clicking on advertisements hosted across a vast network of artificial intelligence-generated websites to defraud online merchants and major advertising networks.
Pedro Falé, a threat researcher with the cybersecurity firm Bitsight, recently uncovered the inner workings of this complex ad fraud ecosystem. The discovery came after Falé registered an expired domain name that had previously been used for device telemetry—a system that periodically collects hardware information and complete lists of installed applications from tens of thousands of streaming sticks plugged into television sets around the world. Specifically, the telemetry domain was tied to a particularly popular brand of low-cost streaming devices widely known as H96.
Upon inspecting the incoming traffic being funneled to the newly acquired domain, Falé discovered a glaring discrepancy. Nearly all of the H96 TV boxes transmitting data were claiming to be mobile phone models manufactured by major global brands, including Samsung, Vivo, Huawei, and Xiaomi.
"We noticed something was wildly wrong," Falé said, recounting the moment telemetry data revealed that factory Android TV boxes were reporting themselves as smartphones.

Further investigation into the metadata revealed that all of the spoofing devices shared the exact same two pre-installed applications. Code analysis traced these applications back to a mainland China-based entity founded in 2019 known as Zhejiang Fengwo IoT Technology Ltd, which operates a broad portfolio of ad-publishing operations under the name Fengwo Group. Digging deeper, Bitsight researchers discovered that the Fengwo Group had registered multiple patents whose operational mechanics matched the inner workings found inside the malicious apps.
According to Bitsight’s published findings, the operation relied on a network of shell identities set up across Hong Kong, Singapore, and various single-person corporate entities to collect monetization revenue, routing the final proceeds back to the parent company in mainland China. The apps themselves function as active orchestrators of a sophisticated ad fraud network, transforming captive H96 streaming devices into automated traffic sources designed to visit and interact with ads on websites operated entirely by the Fengwo Group.
Bitsight’s analysis of these fraudulent websites revealed a network of pages containing machine-generated news articles and computer-rendered graphics covering a diverse array of topics, ranging from finance, health, and education to gaming, music, and food blogs. Crucially, researchers noted that none of these AI-generated web pages displayed advertisements unless the visiting device successfully matched the spoofed mobile profile associated with the compromised H96 streaming sticks.
AI Digital Humans and Low-Skill Automation
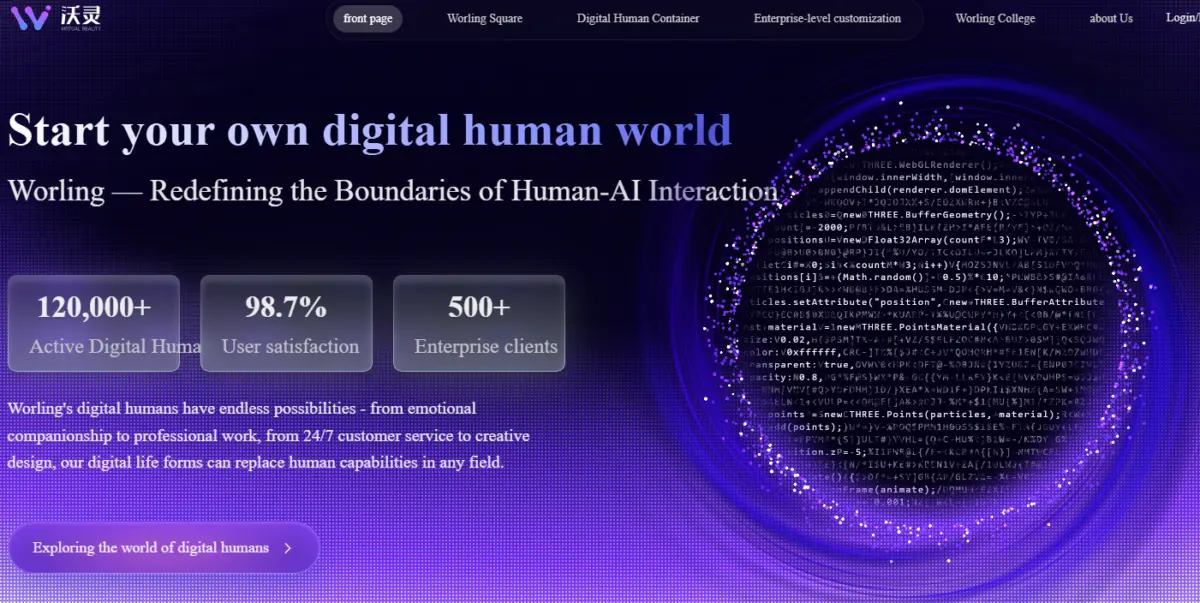
The primary web domain for the Fengwo Group, operating under the address fwgcloud.com, prominently claims that the enterprise is actively redefining the boundaries of human-artificial intelligence interaction. The site boasts that the company has created more than 120,000 "AI digital humans" available for rent for a wide variety of tasks, ranging from digital emotional companionship and 24/7 customer service solutions to automated creative design work.

However, security analysis of the infrastructure tells a very different story. Falé found that the Fengwo Group’s main domain shared identical SSL certificate data with other domains explicitly linked to the applications found on the H96 streaming devices—the very mechanisms responsible for the mobile phone spoofing routines. Furthermore, an internal wiki platform discovered on the domain directly tied the organization to a proprietary implementation of Blockly, a Google-built visual programming language originally created to help children learn the basics of software development.
Bitsight discovered that employees and operators within the Fengwo Group utilized Blockly to rapidly construct their network of sham websites and fraud scripts. By employing a visual interface, low-skilled operators could simply drag blocks of code together within the editor to define specific automated fraud routines without needing any deep understanding of the underlying technical mechanics or code execution. Once a routine was finalized, it was automatically exported as JavaScript and uploaded to cloud storage buckets.
As one internal Fengwo Group developer noted in remarks uncovered by researchers, this modular approach meant that only a small team of highly skilled developers was required to build the initial template execution units. Meanwhile, lower-skilled operators could assemble tasks using those templates, significantly lowering operational technical requirements and drastically reducing the company’s operating costs.
When an H96 streaming stick is selected for a specific fraud task, it is silently pushed the appropriate Blockly module. This code can orchestrate background actions such as launching an invisible web browser, navigating through web pages, managing multiple browser tabs, and ultimately clicking on targeted advertisements. To ensure the TV boxes masquerading as smartphones can successfully interact with these digital advertisements without raising automated anti-fraud suspicions, the Fengwo Group integrated multiple vision and reasoning systems into a unified interface, allowing the bot-driven devices to identify ads and browse sites with human-like behavioral patterns.

TV On for Proxies, TV Off for Ad Fraud
One of the most revealing discoveries made by Bitsight researchers involves the operational duality of the infected streaming devices. The analysis showed that the H96 boxes were utilized either for relaying residential proxy traffic or for participating in active ad fraud, but they never performed both tasks simultaneously.
Researchers concluded that when a user turns on their television and the device detects an active HDMI signal—signifying that the owner intends to use the hardware for its intended purpose of streaming video content—the box functions as a residential proxy. Conversely, when the television is turned off, the hardware seamlessly shifts back into an idle state, waiting to execute background ad fraud tasks.
Falé explained that this division of labor is likely implemented because ad fraud routines are significantly more resource-intensive. Running proxy traffic and heavy ad-clicking automation at the same time would likely degrade device performance, causing noticeable slowdowns or crashes that would alert users to the malicious software running in the background.
Despite repeated, high-profile warnings issued by the Federal Bureau of Investigation and cybersecurity leaders regarding the severe privacy and security risks tied to cheap streaming hardware, major global e-commerce marketplaces—including Amazon, Best Buy, and Newegg—continue to host listings for hundreds of off-brand models. These devices frequently bundle unofficial, modified versions of Google’s Android operating system and are aggressively marketed online through influencers as a convenient loophole to bypass subscription fees for live broadcasts and premium streaming services.

Beyond quietly enlisting home hardware into ad fraud botnets, these inexpensive streaming devices almost universally come pre-installed with residential proxy software. This software essentially auctions off the unsuspecting owner’s residential internet connection to anonymous third-party clients, ranging from aggressive data scrapers and ticket scalpers to malicious cybercriminals.
Because these generic, low-cost TV boxes ship with poor default security controls and lack basic authentication measures, placing them on a home or office network creates wide-ranging vulnerabilities. Earlier this year, proxy tracking firm Synthient documented how complex botnets, such as the Kimwolf botnet, rapidly enslaved millions of similar TV boxes by exploiting intersecting security flaws in both the residential proxy software and the underlying streaming firmware.
Scale of the Operation and Consumer Guidance
Bitsight estimated that approximately 38,000 distinct TV boxes across the globe were actively phoning home to the expired Fengwo Group telemetry domain at the time of the analysis. Based on that conservative figure, researchers calculated that the ad fraud network generates close to $50,000 in daily revenue, a total that does not even account for the substantial secondary income generated through the residential proxy side of the enterprise. Falé emphasized that these financial and device estimates are conservative, as they were derived from telemetry originating from only one of the Fengwo Group’s core historical domains.
As for the company’s grand claims regarding its 120,000 virtual AI humans, Bitsight’s report suggests the figures may simply serve as an elaborate marketing facade designed to obscure the true nature of their infrastructure. Historically, large-scale proxy and botnet operators frequently utilize innocuous corporate facades to mask the true capacity and malicious intent of their digital networks. Attempts by security researchers to contact the Fengwo Group for comment via the email address listed on its public homepage were unsuccessful, as incoming messages were automatically bounced back due to a full inbox.

Security experts reiterate that consumers looking to purchase streaming hardware should exclusively stick to established name-brand manufacturers and exercise caution regarding third-party application installations, as even legitimate smart TV apps have occasionally been found bundling residential proxy modules. Google advises consumers to verify whether a device runs an authentic, Play Protect-certified version of the Android TV operating system by checking official device compatibility guidelines.
Additionally, threat intelligence firms like Synthient maintain publicly accessible tracking lists cataloging internet-of-things devices known to ship with pre-installed proxy software and malicious applications. Security agencies continue to emphasize that these threats extend beyond streaming sticks, affecting other connected consumer hardware such as digital photo frames and smart home accessories purchased from unverified vendors.