It has long been a daunting challenge to determine precisely who is responsible for serving advertisements on visited websites or harvesting personal data from everyday mobile applications. While much of this foundational information has technically remained semi-public, it has traditionally been difficult to parse, remaining heavily walled away within the proprietary repositories of large advertising platforms. That landscape is now shifting with the introduction of DecryptAds, a powerful and free service designed to scrape, correlate, and simplify adtech data to provide immediate insight into the entities tracking users across the digital ecosystem.
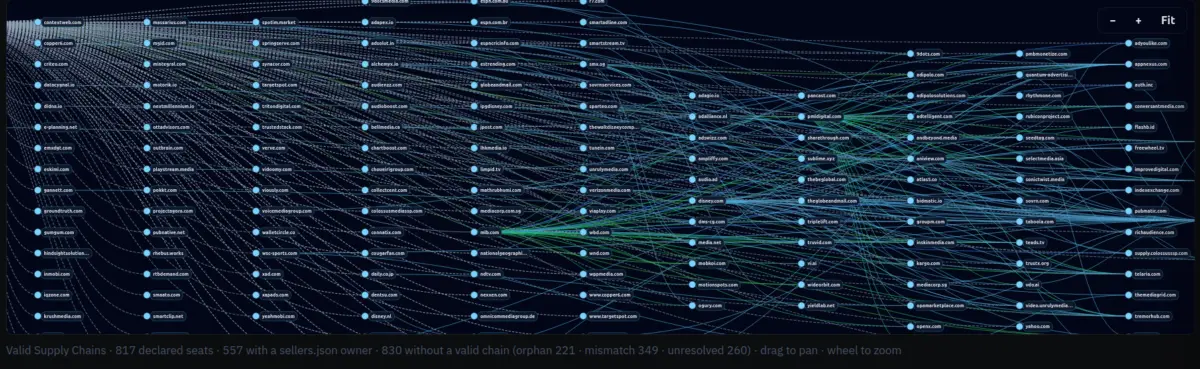
The newly launched platform systematically scrapes the public files that websites and mobile applications maintain to disclose the third-party companies permitted to run advertisements or collect user data. These foundational documents include ads.txt for desktop and mobile websites, app-ads.txt for mobile and smart TV applications, and buyers.json and sellers.json files, which outline the specific entities buying, selling, or reselling advertising inventory for any given digital property.
Zach Edwards, chief research officer for DecryptAds and a threat researcher at the cybersecurity firm Infoblox, explained that he and his co-founders recognized an urgent need for the service because raw adtech data is generally useless in isolation. It only gains value when cross-referenced across multiple sources to construct a complete operational picture of the advertising supply chain for a specific website or application.
Approaching adtech from a security perspective rather than purely a commercial one, Edwards noted that the tool is built to serve privacy and security use cases that have historically been underserved. These applications include tracing the origins of malicious advertisements designed to distribute malware, identifying advertising networks rooted in adversarial nations, and detecting the rapidly growing proliferation of low-quality, AI-generated content farms and companion mobile apps.

According to the platform’s developers, supply-chain integrity issues rarely manifest within a single configuration file. Instead, they typically surface as broken cross-references across ads.txt, app-ads.txt, and sellers.json files; as cloned declaration sets spanning entirely unrelated domains; as suspicious seller removals visible only when comparing multiple exchanges; and as supply paths embedded within server-side bid logs that never appear on a publisher’s authorized seller list.
A sample search on DecryptAds for the prominent sports network ESPN highlights the scale of modern digital tracking. The query reveals 143 distinct advertising partners and 19 registered data broker domains listed within its public authorization files. This visibility into data brokers has gradually improved due to legislation passed in states such as California, Oregon, Texas, and Vermont, which mandate that data brokers register if they commercialize consumer information originating from those jurisdictions. DecryptAds reports that nearly half of these listed brokers collect precise geolocation data from visitors who do not employ ad-blocking technology, while others capture device fingerprints and sensitive personal information.
High-Risk Ad Partners and Geographic Exposure
DecryptAds also illuminates the ultimate beneficiaries and national origins of advertising firms operating within popular applications and websites, applying explicit warnings when partners are based in high-risk jurisdictions such as China and Russia, or in countries maintaining close financial and political alignments with them, including Cyprus and the United Arab Emirates.
For instance, the platform indicates that ESPN maintains business relationships with four advertising entities based in Russia, China, or the UAE. Among them is Between Digital, an adtech firm that lists an official corporate address in New York. However, its DecryptAds dossier flags it as a Russian enterprise, documenting that its publisher payout offers are processed through Alfa Bank, Russia’s largest private commercial bank, which was placed under United States economic sanctions following the invasion of Ukraine.

Similar risk profiles emerge when examining other prominent web properties. A search across multiple military news websites, including publications covering the U.S. Army, Air Force, Navy, Marine Corps, and federal workforce, indicates that they all permit Between Digital to serve advertisements and track users, alongside entities based in the UAE and the ownership secrecy jurisdiction of Panama. DecryptAds reports that Between Digital actively collects advertising data across approximately 55,000 partner websites.
Pivoting further into Between Digital’s app-ads.txt disclosures reveals hundreds of domains featuring lightweight, web-based games frequently interrupted by commercial breaks. Edwards noted that the company’s own public declarations indicate it acts as both a publisher and a reseller on roughly two-thirds of its portfolio. This dual positioning allows firms to operate on both sides of the bidding equation, creating potential conflicts of interest by directing client ad spend toward owned-and-operated properties or internal infrastructure.
A similar analysis of the Opera web browser, which remains majority-owned by the Chinese firm Kunlun Tech despite maintaining its operational headquarters in Oslo, Norway, highlights extensive foreign data-broker integration. Opera’s profile identifies 27 registered data brokers collecting user information, including adtech partners located in the UAE, China, Cyprus, Russia, Hong Kong, and Ukraine, representing a fraction of the total third-party vendors declared in its configuration files.
Legal Dossiers and Quiet Removals
Among the platform’s more advanced investigative features is its Legal Dossier lookup. Although individual searches can take several minutes to compile, the tool aggregates comprehensive ownership histories, domain registration timelines, organizational aliases, and interconnected relationships linking adtech companies, websites, and applications.

This capability maps directly to broader supply-chain vulnerabilities recently uncovered by security researchers. For example, investigations into popular H96 TV streaming sticks revealed that the devices quietly monetize user internet connections while spoofing mobile device signatures to interact with advertisements on automated, AI-generated content farms. Researchers concluded that the Chinese entity behind these streaming applications, the Fengwo Group, simultaneously operated the network of low-quality websites receiving automated traffic from thousands of compromised devices.
Legal dossiers for dormant domains associated with the Fengwo Group demonstrate shared seller identification numbers linking them to obscure gaming websites, which in turn connect to hundreds of active web properties operating within Russia’s Yandex advertising ecosystem.
To combat opacity within the industry, DecryptAds also incorporates a quiet removals feed. When major advertising exchanges suspect an advertiser of participating in fraudulent clicks or distributing malicious content, they frequently remove the offender from their approved partner lists without public notification, allowing compromised entities to continue operations elsewhere. By tracking sellers.json removals across multiple exchanges simultaneously, the platform exposes these hidden administrative actions and provides transparency regarding suspicious vendor bans.
Malvertising, Artificial Content Farms, and Industry Solutions
Malvertising—the injection of malicious code or deceptive redirects into legitimate ad spaces—remains a persistent threat within the digital advertising ecosystem. However, researchers emphasize that these attacks rarely occur on high-traffic, heavily monitored destinations like major news outlets, which employ dedicated third-party security tools and continuous auditing to intercept compromised ads. Instead, malicious actors frequently target newly generated, AI-created content farms that lack protective infrastructure and rely on low-quality monetization partners.

These AI content farms typically feature automated, machine-generated articles spanning home improvement, recipes, automotive topics, and consumer technology. According to Edwards, organizations targeted by malicious advertising campaigns often fail to realize that the vector of compromise is frequently disclosed directly within a website’s ads.txt file. Effectively addressing both malvertising and the proliferation of low-quality content farms will ultimately require broader data sharing across major advertising networks, particularly concerning server-side supply chain objects that detail the complete transactional path of an ad impression from publisher to final buyer.
In response to these systemic tracking and security challenges, security professionals continue to recommend the use of robust ad-blocking technologies at the browser or network level. Desktop users frequently rely on open-source extensions such as uBlock Origin Lite, while mobile and network-level solutions, including Pi-hole implementations, offer centralized protection across connected environments. Beyond blocking commercial interruptions, these tools limit the continuous data harvesting executed by advertising networks and data brokers operating in the background of modern web and mobile applications.